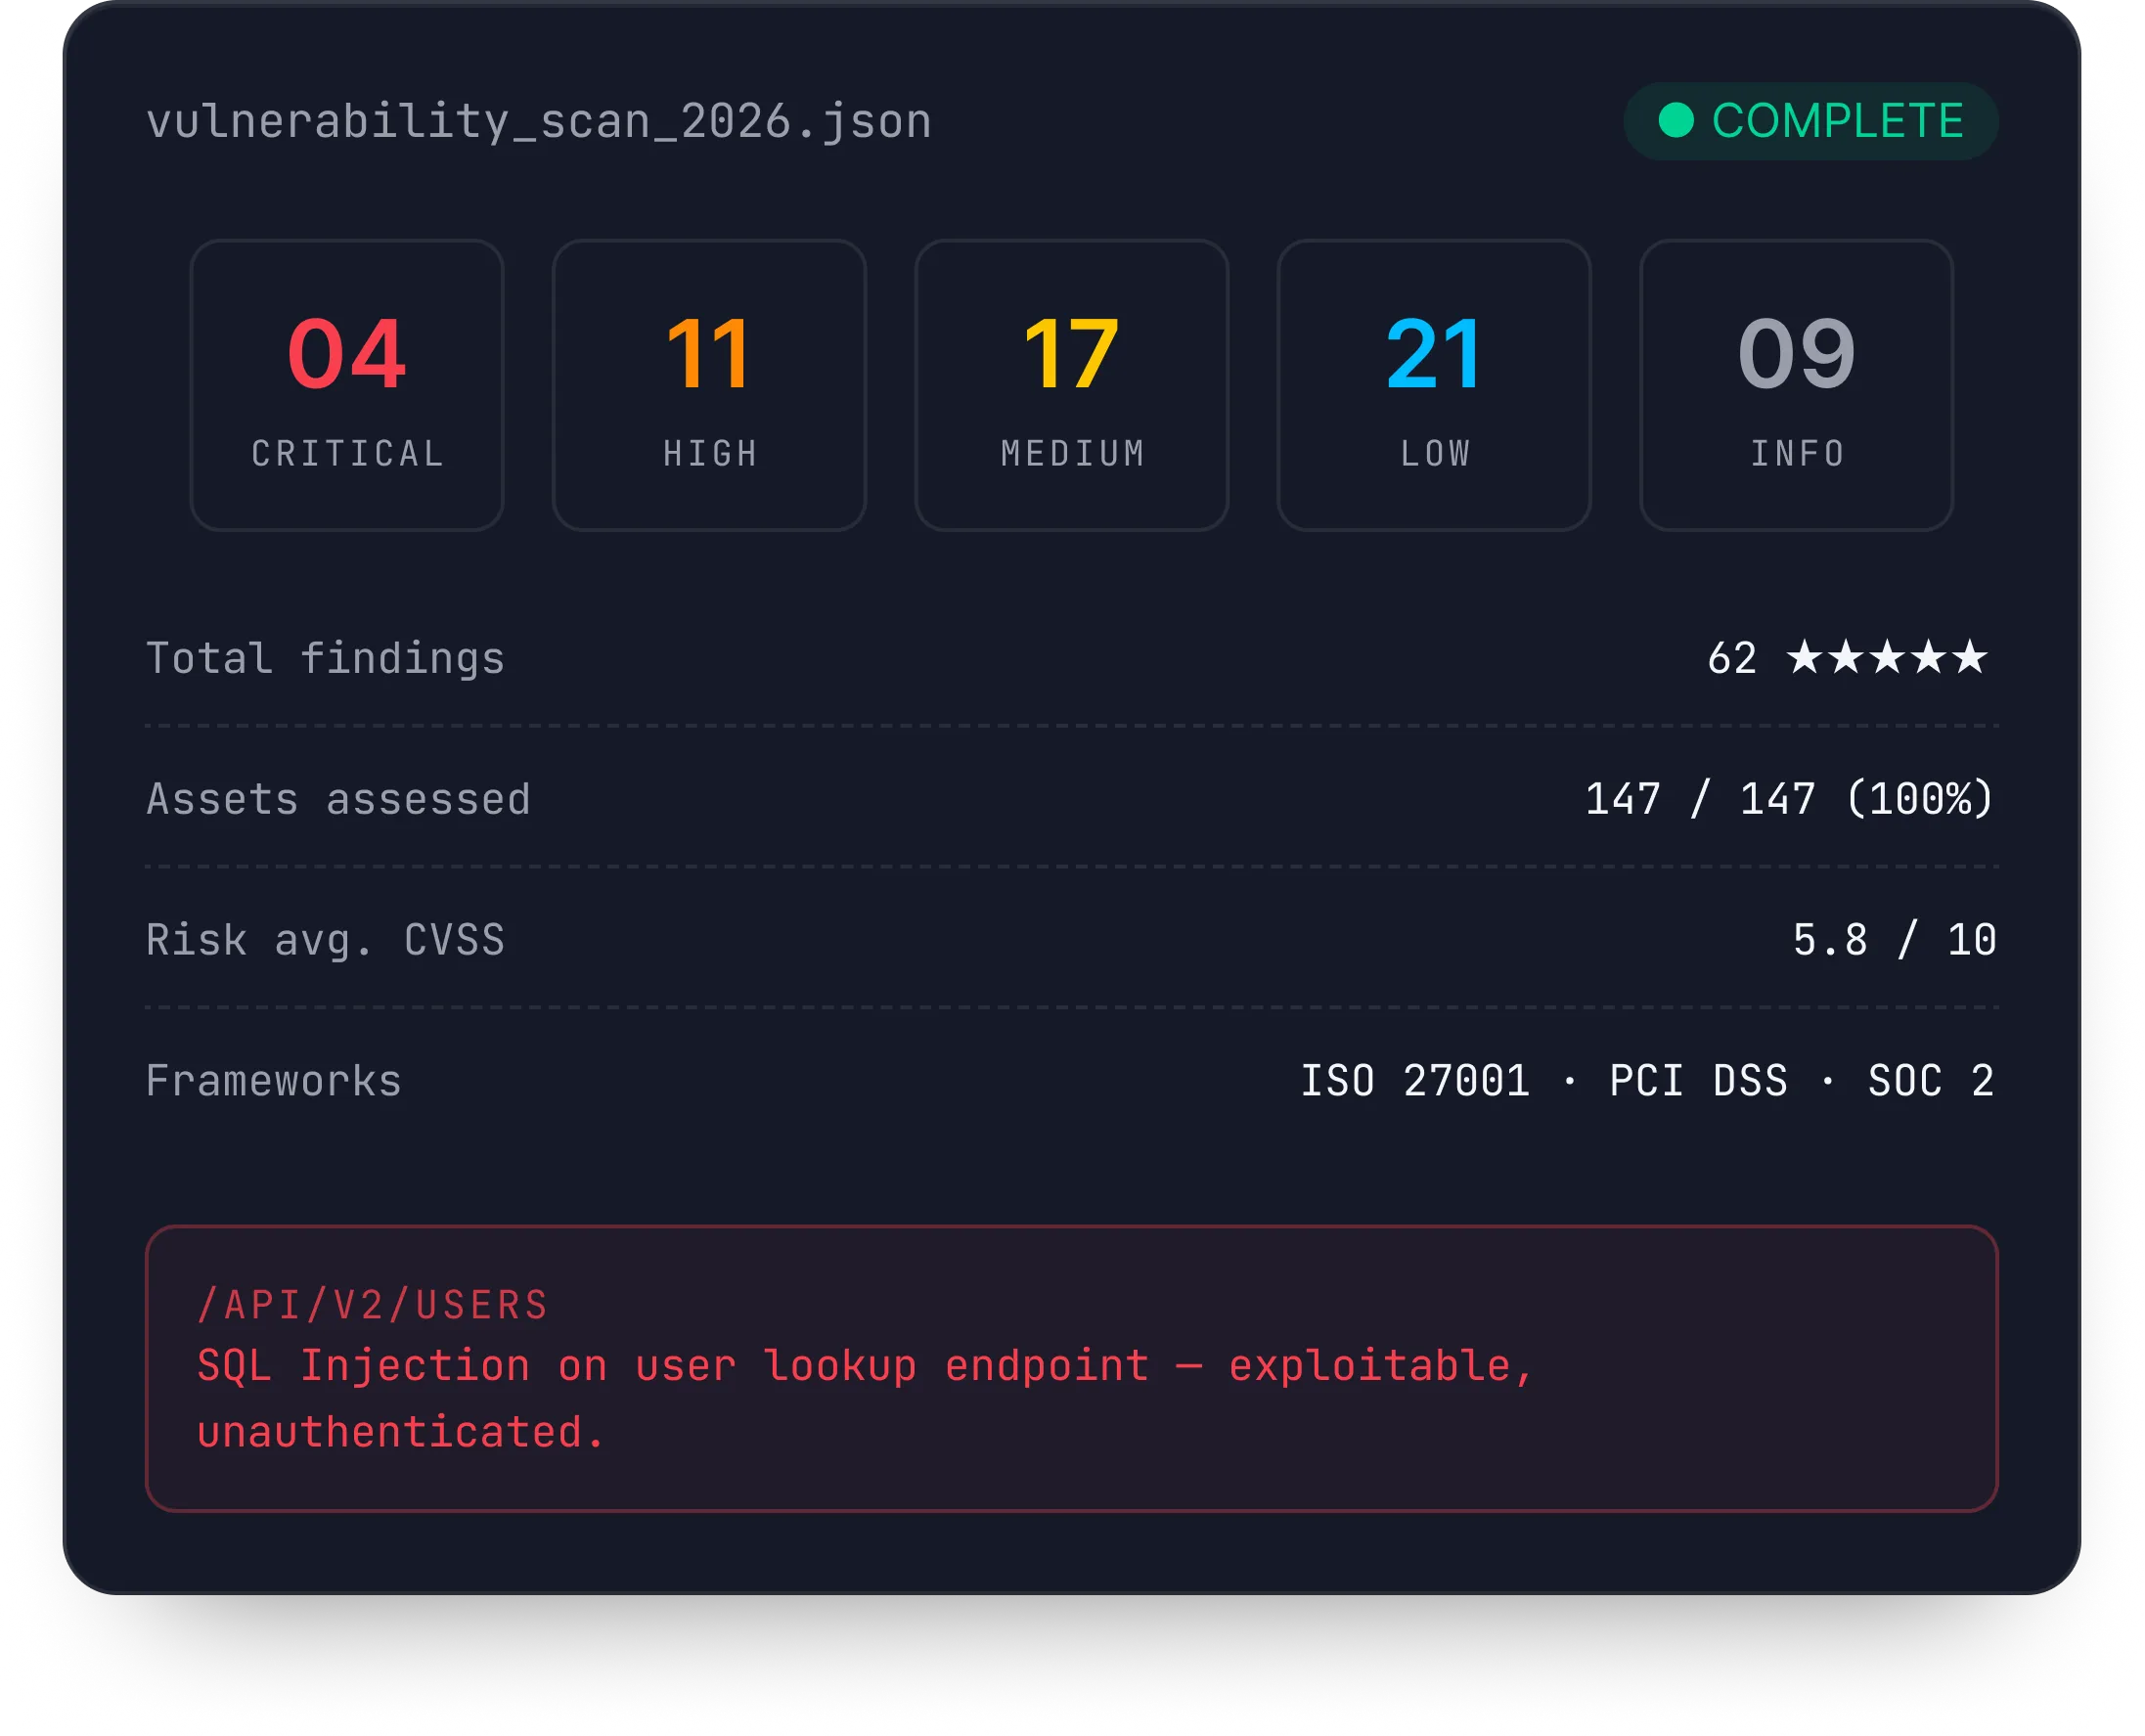
Find every weakness — before it becomes a breach.
1–2 wk
Typical timeline
CVSS v3.1
Severity scoring
30 days
Free retest
A complete map of your risk surface.
Asset discovery
Full inventory of internet-facing and internal assets, services, and exposed endpoints — including shadow IT.
CVE matching
Every service is mapped against known CVE databases and threat intel feeds for outdated and exploitable software.
Risk prioritization
CVSS-scored findings ranked by exploitability and business impact — so your team knows what to fix first.
Audit-ready report
Executive summary plus detailed technical findings, mapped to ISO 27001, PCI DSS, and SOC 2 controls.
Every layer of your stack — assessed.
Network & infrastructure
- External perimeter scan
- Internal network sweep
- Firewall & VPN config audit
- Open ports & exposed services
Web applications
- OWASP Top 10 baseline
- Authenticated crawls
- API endpoint discovery
- TLS / cert hygiene
Cloud (AWS / Azure / GCP)
- IAM policy review
- Public storage buckets
- Misconfigured security groups
- CIS benchmark deltas
Databases & data stores
- Default credentials
- Exposed admin interfaces
- Backup / dump exposure
- Encryption at rest
Containers & Kubernetes
- Image CVE scanning
- Kubelet & API exposure
- RBAC review
- Secrets & ConfigMaps
Identity & access
- MFA coverage
- Privileged account audit
- Stale credentials
- SSO misconfiguration
A 4-stage VAPT process — from scoping to retest.
No black-box engagements. You see what we test, what we find, and how to fix it.
Scope & rules of engagement
Free consultation. We define targets, depth, timeline, and out-of-scope assets in writing.
Vulnerability assessment
Asset mapping, attack surface enumeration, and scanning to identify all weaknesses.
Manual exploitation
Senior testers chain vulnerabilities, validate real exploitability, and capture proof-of-concept.
Report & retest
Audit-ready report with risk-scored findings, remediation steps, and a free retest after fixes.
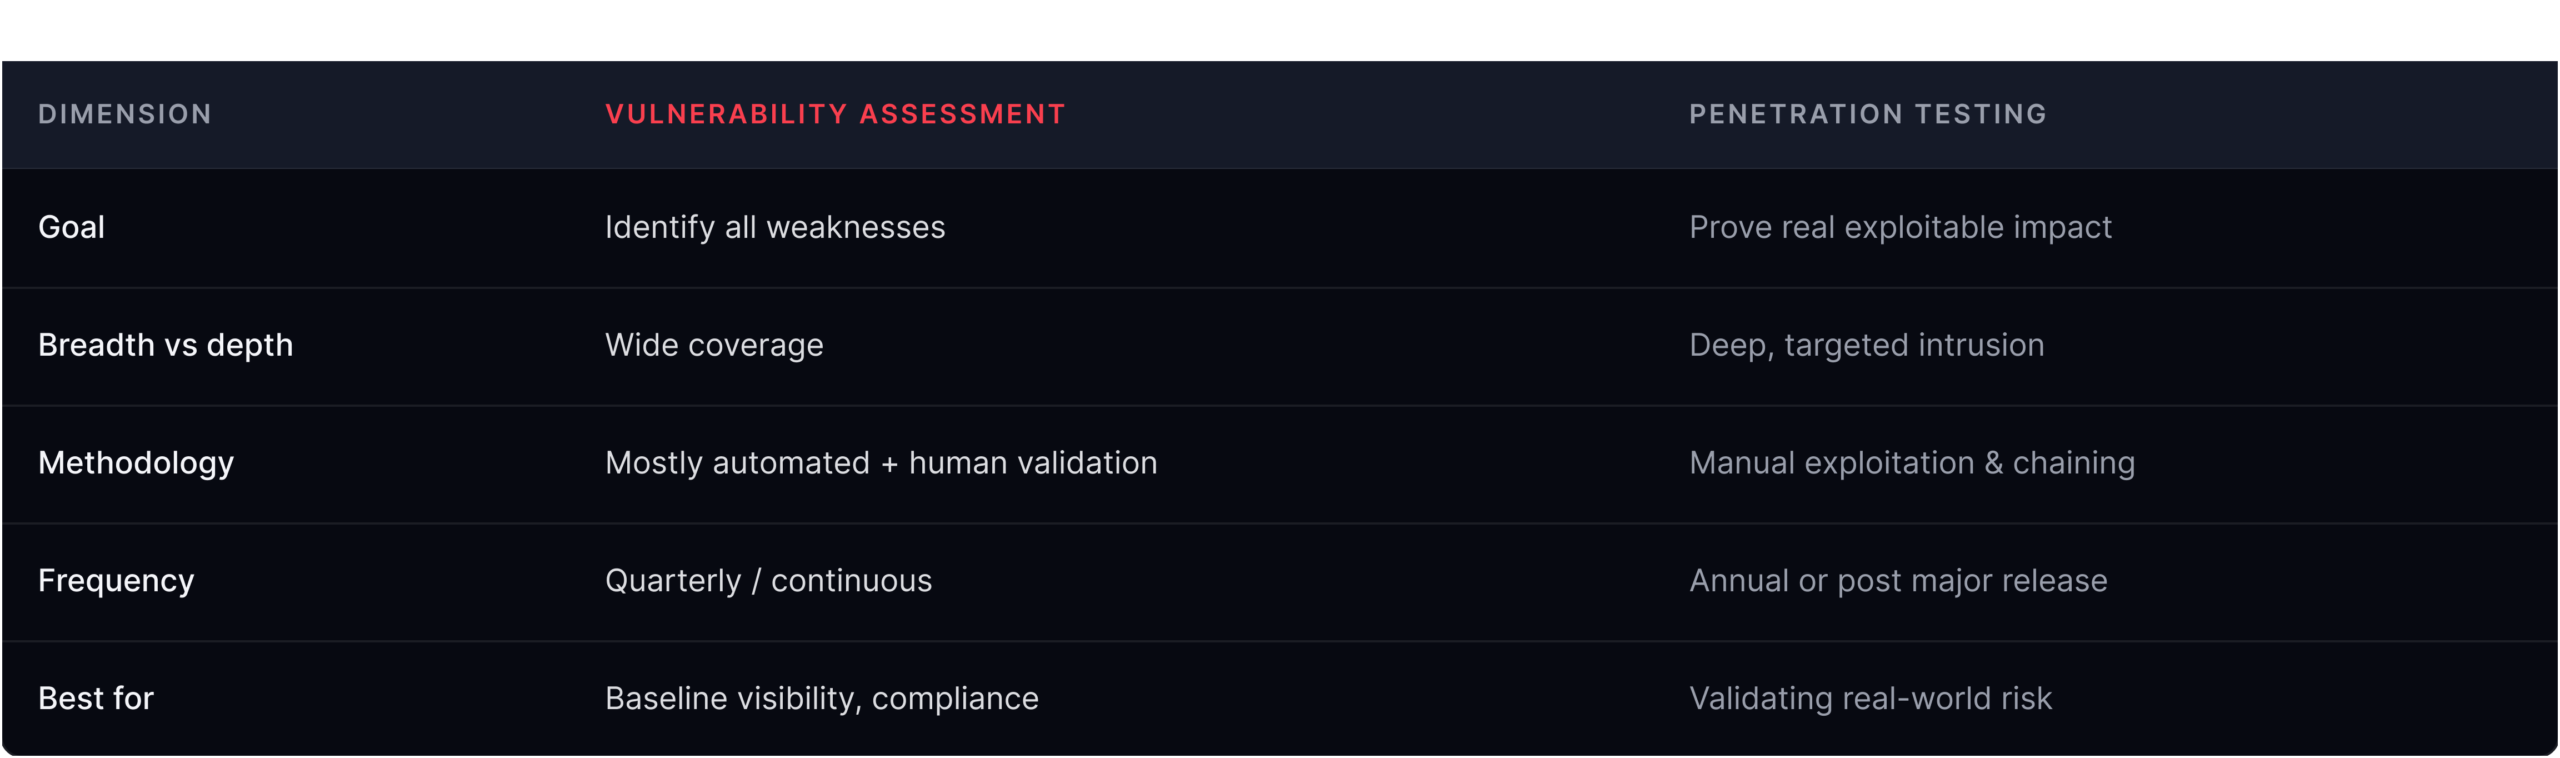
When VA is enough — and when you need a pentest.
Common questions about VAPT & penetration testing.
Don’t see your question? Reach out — we’ll answer within 24 hours.
What is the difference between vulnerability assessment and penetration testing?
Should I get a vulnerability assessment, a pentest, or both?
How much does VAPT cost in Pakistan?
How long does a typical VAPT engagement take?
Do you provide retesting after we fix the vulnerabilities?
Will the testing disrupt our production systems?
Are your reports compliant with international standards?
Do you serve clients outside Pakistan?
Ready to find your vulnerabilities before someone else does?
Free 30-minute consultation. We’ll review your stack, discuss scope, and send a tailored quote within 24 hours.
