We don't just find bugs — we exploit them.
OSCP
OSWE
CRTP
CEH
OWASP
NIST 800-115
NIST 800-115
PTES
ISO 27001
Built for modern, complex stacks.
Web application pentest
Manual testing of authentication, business logic, and access control for your websites, dashboards, and SaaS platforms — beyond what scanners catch.
Network penetration testing
Internal and external network assessments. We probe firewalls, servers, switches, and exposed services for the gaps that lead to lateral movement.
Cloud security testing
Configuration audits and offensive testing for AWS, Azure, and Google Cloud. We find misconfigured S3 buckets, IAM gaps, and exposed metadata before they cost you.
Mobile app penetration testing
Static and dynamic analysis for Android and iOS apps. We test storage, transport, runtime tampering, and reverse-engineering resistance against OWASP MASVS.
Secure Code Review / SAST
Secure Code Review & SAST that identifies security flaws in your code early—so your team can fix them before attackers exploit them.
Social Engineering / Phishing Simulation
Realistic phishing and social engineering simulations that reveal human vulnerabilities and strengthen your organization’s security awareness.
AI / LLM Security Testing
Test AI and LLM applications for prompt injection, data leakage, insecure outputs, and other emerging AI security risks.
Dark Web Monitoring & Threat Intelligence
Monitor the dark web and open-source intelligence for leaked credentials, exposed data, and emerging threats targeting your organization.
Red Team / Adversary Simulation
Adversary simulations designed to challenge your people, technology, and defenses against realistic attack scenarios.
IoT / OT / Hardware / Mainframe
Specialized security testing for connected devices, operational technology, hardware, and legacy systems where conventional penetration testing falls short.
A 4-stage VAPT process — from scoping to retest.
No black-box engagements. You see what we test, what we find, and how to fix it.
Scope & rules of engagement
Free consultation. We define targets, depth, timeline, and out-of-scope assets in writing.
Vulnerability assessment
Asset mapping, attack surface enumeration, and scanning to identify all weaknesses.
Manual exploitation
Senior testers chain vulnerabilities, validate real exploitability, and capture proof-of-concept.
Report & retest
Audit-ready report with risk-scored findings, remediation steps, and a free retest after fixes.
What you walk away with.
Executive summary
1-page board-level risk narrative with business impact, not jargon.
Technical findings report
Every vulnerability with reproduction steps, screenshots, and CVSS rating.
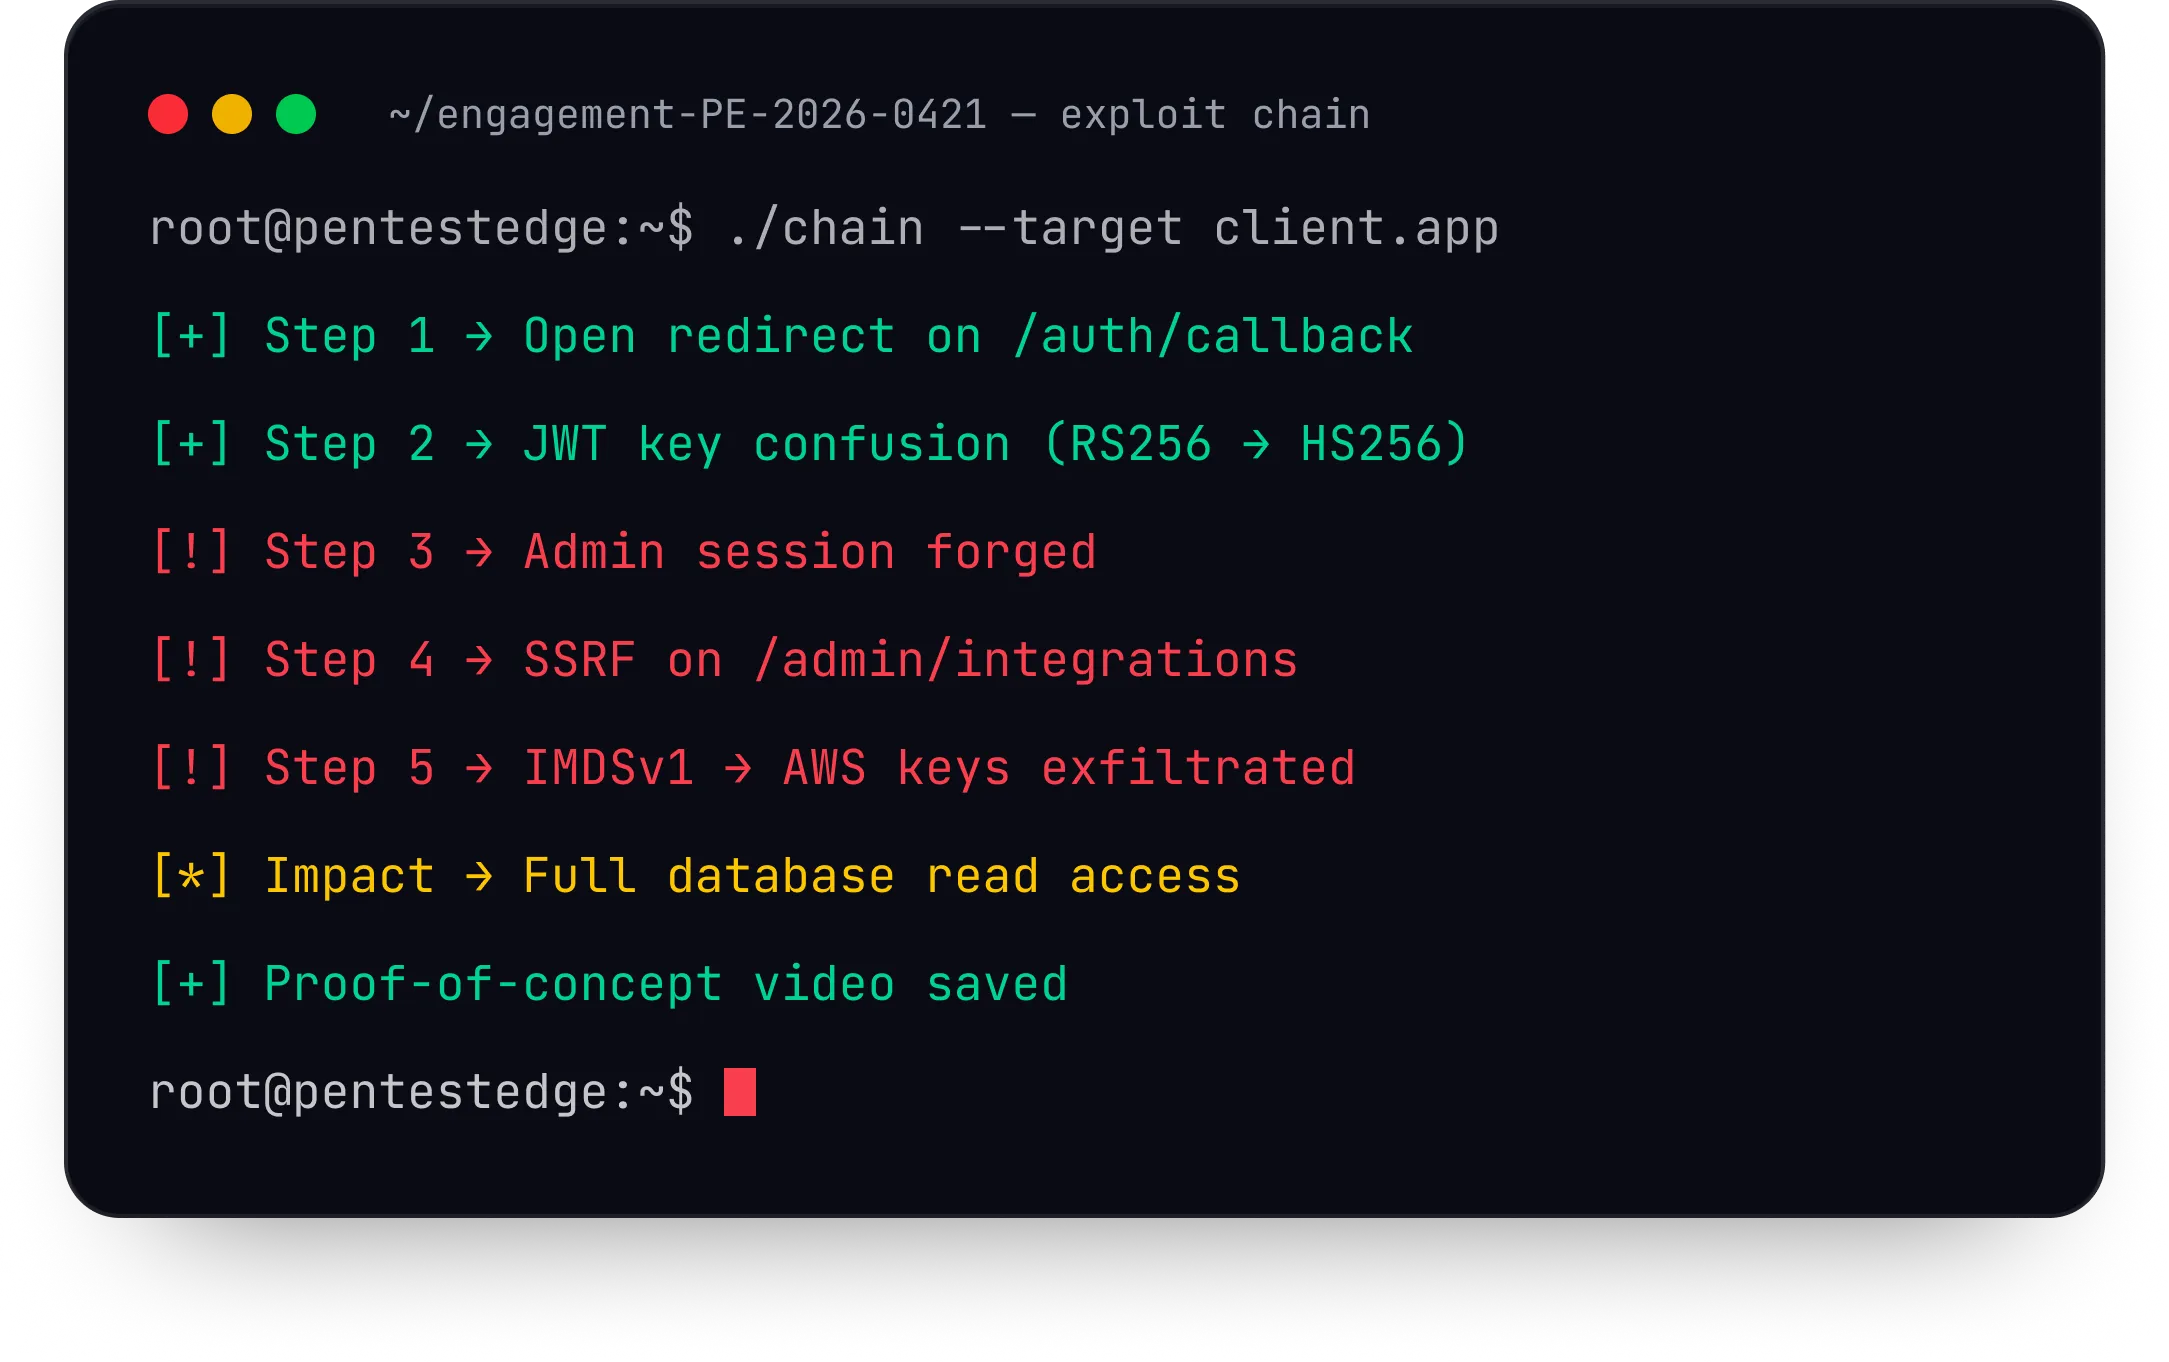
Exploit chain walkthrough
Video PoC and step-by-step kill-chain for critical issues.
Remediation roadmap
Prioritized fix plan with code samples and config guidance.
Compliance mapping
Findings mapped to OWASP, NIST, PCI DSS, ISO 27001, SOC 2 controls.
Free retest
Re-validation of fixed findings within 30 days — included.
Real adversaries — on contract.
100% manual exploitation
Scanners are a starting point, not a finish line. Every CRITICAL finding is exploited and validated by a human.
Real-world attack chains
We don't just report bugs in isolation. We chain them — the way a real attacker would — to prove blast radius.
Developer-grade reporting
Code snippets, config diffs, and reproduction steps. Findings drop straight into your sprint backlog.
Black, grey, white — your call.
Black-box
Zero knowledge
Simulates an unauthenticated external attacker with no insider information.
Best for
External attack simulation, perimeter validation
Grey-box
Limited insider knowledge
Low-privilege credentials and partial documentation provided. Most realistic for SaaS apps.
Best for
Web apps with auth, customer-facing portals
White-box
Full transparency
Source code, architecture diagrams, and admin access shared. Highest coverage per hour.
Best for
Pre-release audits, regulatory engagements
Common questions about VAPT & penetration testing.
What is the difference between vulnerability assessment and penetration testing?
Should I get a vulnerability assessment, a pentest, or both?
How much does VAPT cost in Pakistan?
How long does a typical VAPT engagement take?
Do you provide retesting after we fix the vulnerabilities?
Will the testing disrupt our production systems?
Are your reports compliant with international standards?
Do you serve clients outside Pakistan?
Ready to find your vulnerabilities before someone else does?
Free 30-minute consultation. We’ll review your stack, discuss scope, and send a tailored quote within 24 hours.
